Trust Breaks Before Systems Do: Professor Kai London on Governing Cyber Risk Before It Governs You
By the Daneborg Times Technology Desk
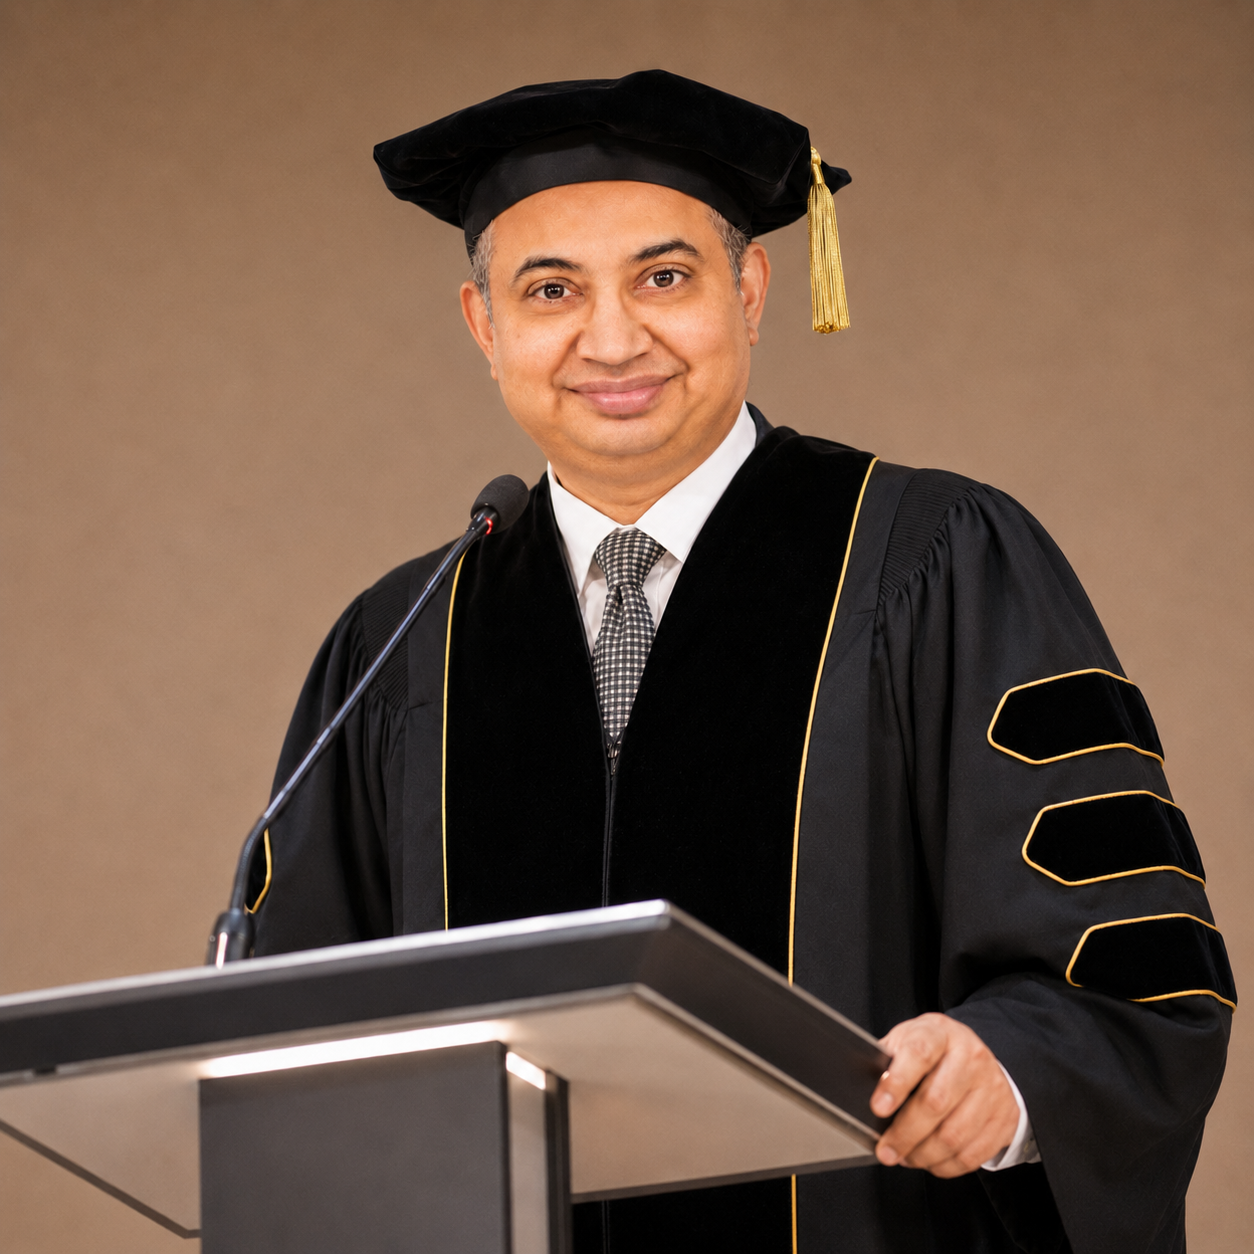
When a cyber crisis finally becomes visible — the outage, the ransom note, the regulator's letter — it feels sudden. It almost never is. “Trust breaks before systems do,” says Professor Kai London, a senior CISO and board-level security executive. “By the time you see the failure, the real fault line opened months earlier, on a weakness nobody was watching. The visible collapse is the last act, not the first.”
“Every board should be able to walk into a room and answer five questions: what could break, who owns it, what it would cost, which control holds it, and where the evidence is. If you cannot answer those, you are not governing cyber risk — you are hoping.”
The fault lines beneath the surface
London's central metaphor is seismic. Organisations, he argues, accumulate stress along hidden fault lines — an unpatched dependency, an over-privileged account, a supplier with poor security, a control that everyone assumes works but nobody has tested. Pressure builds invisibly until a trigger releases it. “The tremors are there long before the quake,” he says. “The discipline is learning to read them.”
He points to a familiar cast of recent incidents — a healthcare clearinghouse whose outage rippled across an entire system, manufacturers and retailers brought to a standstill, a finance team deceived by a deepfaked video call, a supply-chain compromise that spread through trusted software. In each, London observes, the technology was not exotic. The failure was one of governance: a risk that was known, or knowable, and not owned.
From reacting to instrumenting
The remedy London prescribes is not another product but a set of instruments a board can actually use. Map the trust fault lines — the dependencies and single points of failure that, if broken, break the business. Load-test the controls that are supposed to hold those fault lines, rather than assuming they will. Model the blast radius of a failure before it happens. Put a clock on containment, so the organisation knows how fast it can stop the spread. And keep a “defensibility ledger” — the evidence that, when the regulator or the court asks, proves the organisation acted reasonably. “Instrumentation turns cyber risk from a vague anxiety into a governed number,” he says.
The supply chain is now the fault line
Increasingly, London notes, the most dangerous fault lines run outside the organisation's own walls. “Your security is now the weakest update in your supplier's pipeline, and the weakest login at your service provider,” he says. Modern breaches propagate through trusted relationships — software vendors, managed service providers, cloud platforms — precisely because those relationships are trusted. Governing cyber risk, therefore, increasingly means governing the risk you have outsourced. “You can delegate the work,” he says, “but you cannot delegate the accountability.”
Leading indicators over lagging ones
A recurring theme in London's thinking is the difference between leading and lagging indicators. Most organisations measure cyber risk by what has already gone wrong — incidents, downtime, losses. That, he argues, is like driving by looking in the mirror. The instruments that matter are the ones that reveal accumulating stress before the break: the growth of unmanaged privilege, the drift of unpatched systems, the concentration of dependence on a single provider, the gap between the controls you claim and the controls you have tested. “Measure the tremors,” he says, “not just the wreckage.”
A discipline the whole organisation can share
Crucially, London insists this is not solely a specialist's job. Executives, employees, and even job-seekers and customers all have a stake in whether trust holds. His work deliberately translates cyber risk into plain language precisely so that a non-technical director, an operations manager and a front-line employee can each understand their part. “Cyber resilience fails when it lives only in the security team,” he says. “It succeeds when the whole organisation can name the fault lines and knows what to do when one starts to move.”
Governing before the quake
For boards, London's counsel is to act while the ground is still quiet. Identify the fault lines now. Assign owners. Test the controls. Rehearse the response. Build the evidence trail. “The organisations that survive a cyber crisis are almost never the ones with the most technology,” he concludes. “They are the ones that governed the risk before it governed them — that read the tremors, and reinforced the fault lines, before the quake arrived.”
About Professor Kai London. Professor Kai London is a senior technology, security and transformation executive with more than 25 years of board- and C-suite leadership across banking, aviation, defence, government and critical national infrastructure. He is Founder & CEO of Quantum AI Systems Security, an Honorary Professor in Cybersecurity, AI & Quantum Computing, and a UCL researcher, holding CISSP, CISM, CCISO, ISO 27001 Lead Auditor, ISO 42001, DORA and NIS2 credentials. He is available for board advisory, NED and interim or fractional CISO/CIO/CTO mandates across the UK and internationally. Learn more at professorkailondon.com.


Comments
Post a Comment