DORA and NIS2 in Plain English: What Every Board Must Do Now, According to Professor Kai London
By the Daneborg Times Technology Desk
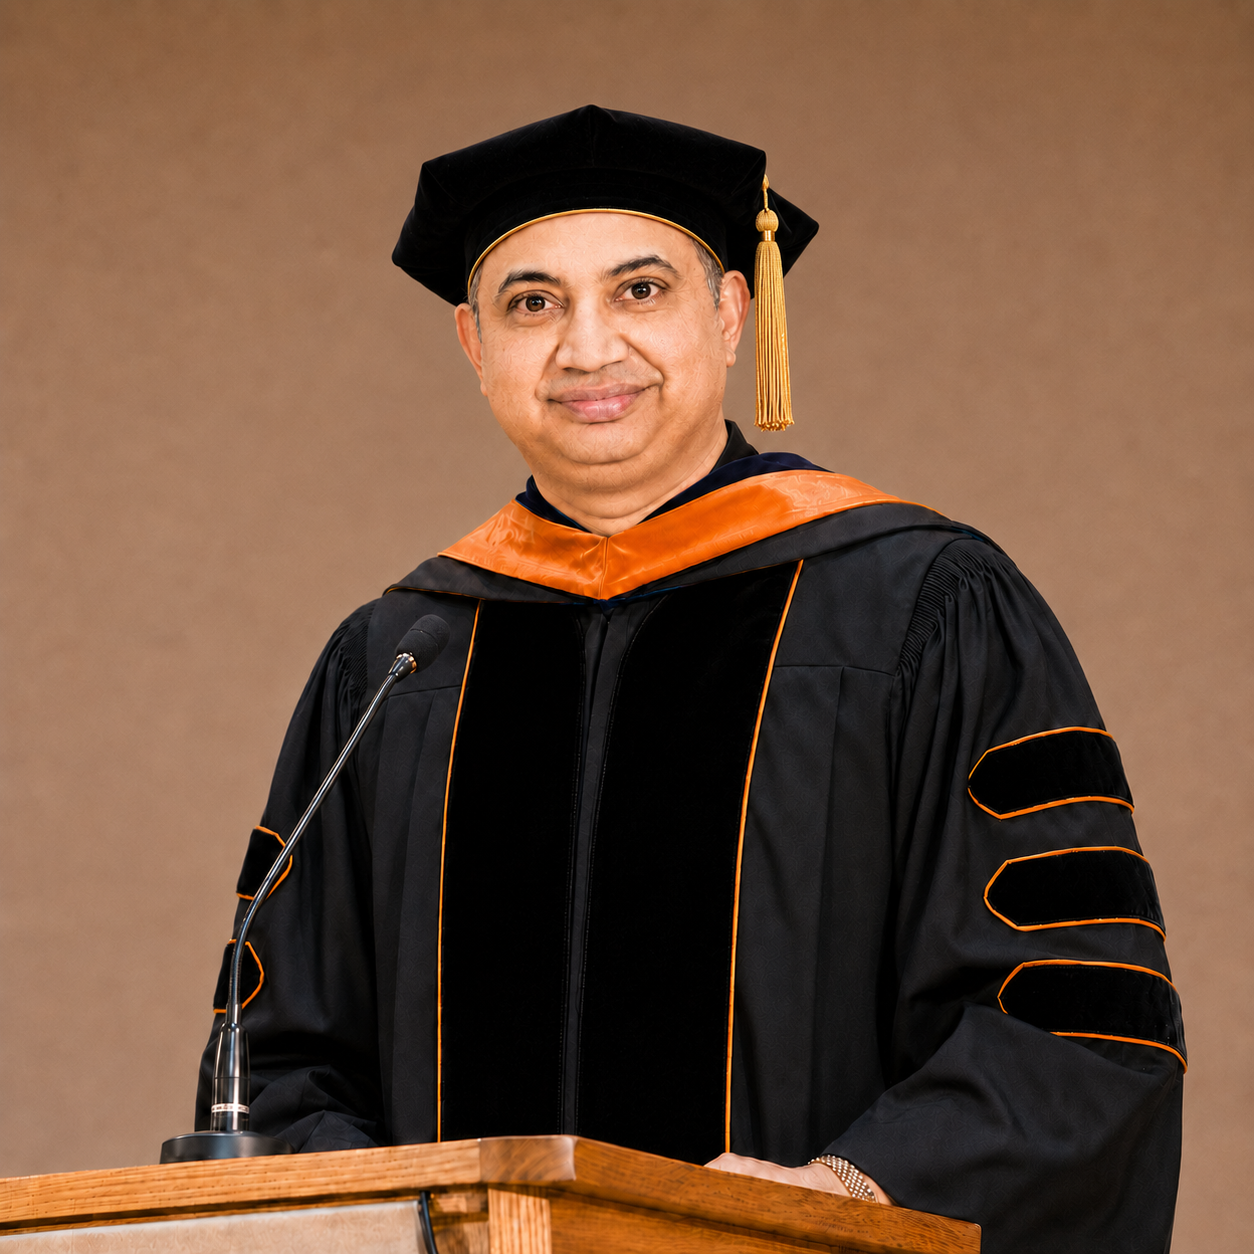
Two regulations have quietly become the most consequential items on many European boardroom agendas: the Digital Operational Resilience Act (DORA) and the second Network and Information Security Directive (NIS2). They are long, technical and easy to delegate into a compliance backwater. That, warns Professor Kai London, a senior CISO and board advisor, would be a serious mistake. “These are not IT paperwork exercises,” he says. “They put personal accountability for cyber resilience on the board itself.”
“DORA and NIS2 mark the moment cyber stopped being something the board hears about after the fact, and became something the board is answerable for. The regulators have moved the question from ‘did you have a policy?’ to ‘can you prove it worked?’”
What DORA actually asks
DORA applies to the European financial sector and the technology providers that serve it. Stripped of jargon, London says, it asks four things. Can you keep critical services running through a disruption? Can you detect, manage and report incidents within tight timelines? Do you test your resilience — genuinely, including through threat-led exercises — rather than assume it? And do you know, and manage, the risk sitting in your third-party technology providers, right down to the concentration risk of everyone depending on the same few cloud platforms? “DORA treats resilience as an outcome you must evidence,” he explains, “not a control you can tick.”
What NIS2 actually asks
NIS2 casts a wider net, covering essential and important entities across energy, transport, health, water, digital infrastructure and more. Its demands rhyme with DORA's: risk management measures proportionate to the threat, prompt incident reporting, supply-chain security, and — crucially — management accountability. “NIS2 is explicit that senior management must approve and oversee cyber-risk measures, and can be held liable for failures,” London notes. “It is difficult to imagine a clearer signal that this belongs on the board's agenda.”
The common thread: prove it
What unites the two regimes, London argues, is a shift from intention to evidence. Both expect organisations not merely to have controls but to demonstrate that those controls function under real conditions. “A regulator no longer wants to read your policy,” he says. “They want to see the incident you handled, the timeline you met, the test you ran, the supplier risk you closed. Evidence, not assertion.”
The five questions every director should be able to answer
London distils the obligations into a short board self-test. First: what are our most critical services, and how long can we survive without them? Second: if we suffered a serious incident today, could we detect it, contain it, and report it within the required timeframe? Third: which third parties could take us down, and what happens if one of them fails? Fourth: when did we last genuinely test our resilience, rather than assume it? And fifth: can we prove all of the above to a regulator with documented evidence? “If the honest answer to any of those is ‘I'm not sure,’ that is precisely the work,” he says.
Turning compliance into advantage
London is keen to reframe the exercise. Treated as a grudging cost, DORA and NIS2 become an expensive drag. Treated as a discipline, he argues, they become a competitive asset. “An organisation that can genuinely demonstrate operational resilience wins the trust of regulators, partners and customers — and increasingly wins the contracts that require it,” he says. “Resilience you can prove is a differentiator, not just a defence.”
Where boards should start
For organisations still finding their footing, London recommends beginning with a candid mapping exercise: identify the critical services, the dependencies beneath them, and the third parties they rest on. From there, build the incident-response and reporting muscle to meet the timelines, and test it under pressure. Much of the exposure, he emphasises, sits in the supply chain — in the vendors and platforms an organisation does not build itself. “Your resilience is only as strong as the weakest provider you cannot live without,” he says.
For sectors that underpin daily life — finance, energy, transport, health — the era of treating cyber resilience as a technical footnote is over. DORA and NIS2 have made it a matter of governance, accountability and evidence. The boards that adapt fastest, London concludes, will be the ones that stop asking whether they have a policy, and start proving that it works.
About Professor Kai London. Professor Kai London is a senior technology, security and transformation executive with more than 25 years of board- and C-suite leadership across banking, aviation, defence, government and critical national infrastructure. He is Founder & CEO of Quantum AI Systems Security, an Honorary Professor in Cybersecurity, AI & Quantum Computing, and a UCL researcher, holding CISSP, CISM, CCISO, ISO 27001 Lead Auditor, ISO 42001, DORA and NIS2 credentials. He is available for board advisory, NED and interim or fractional CISO/CIO/CTO mandates across the UK and internationally. Learn more at professorkailondon.com.


Comments
Post a Comment